Cross-Site Request Forgery
A malicious attack that exploits a security vulnerability to an authenticated user via a forged request that tricks the user into performing an unintended action, such as changing an account password or transferring money into an attacker's account.
Cross-Site Request Forgery (CSRF) is a security vulnerability where an attacker tricks a user into performing actions without their consent. In construction management software, protecting against CSRF is crucial to safeguarding sensitive data and maintaining the integrity of project information.
Used in a sentence
Implementing security measures prevents cross-site request forgery in our project management software.
Synonyms/variation
CSRF
Stay updated on what’s happening in construction.
Subscribe to Blueprint, Procore’s free construction newsletter, to get content from industry experts delivered straight to your inbox.
Learn MoreLearn more about Cross-Site Request Forgery
Does your asset management workflow actually work?
Every fixed asset installed on a project generates data long before handover. Is your team capturing it as it happens, or scrambling to reconstruct it after the fact? That question matters more than it used to because by the time a project gets handed over to an owner, it usually has thousands of components. Fortunately, […]
From spec book chaos to single source of truth
Picture this: An expansion is going in directly beside a high-volume line that cannot stop producing. Structural steel lands in March, mechanical completion is promised for August, and your only window to tie into existing process utilities is a planned 14-day shutdown that’s been locked on the master production calendar for 11 months. Miss that […]
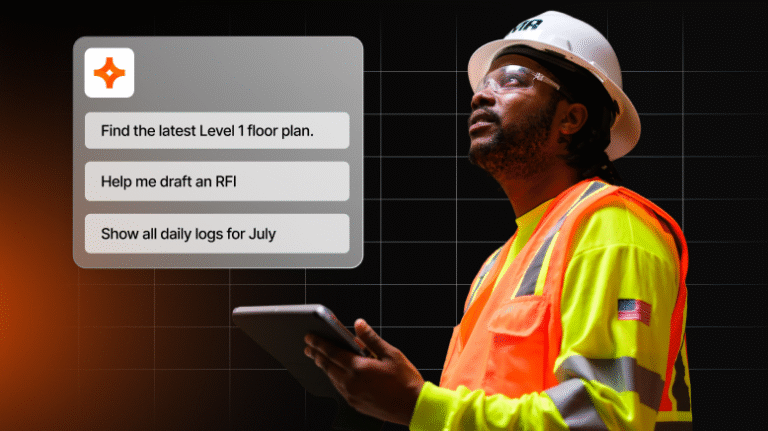
New tech tools without the onboarding: How AI can help break blockers
Huge swaths of the construction industry have digitized over the last decade, many propelled by the efficiency gains tech delivers. Still, software adoption often stalls, hitting the same barrier time and again. That blocker? The learning curve. Training team members how to use the tech typically requires time and effort. AI is no exception here. […]

How leading retailers optimize capital portfolio execution
Most retailers are managing fast-moving capital portfolios with a key problem: Project data lives in their GC’s systems and not their own. Without owning that data, they’re perpetually reactive on cost, schedule, and capital decisions. We spoke with capital program leaders and advisory experts — including Sara Angus, Field COO at Procore and former Director […]
How can we improve this glossary entry?
By clicking this button, you agree to our Privacy Notice and Terms of Service.